
The “Dream Job” Cyberattack: Why Cybersecurity Awareness Matters for Crypto Companies
An attack reportedly involving $6.3 billion highlights a growing cybersecurity threat in the crypto sector. Just two days before the incident, the Crypto Valley Association was already bringing the community together to discuss cybersecurity challenges.
A job offer that looks too good to be true can become the starting point of a major cyberattack.
According to Binance’s November 2026 incident report, an attack involving approximately $6.3 billion began with what appeared to be a legitimate job opportunity. The case reflects a growing threat described by Switzerland’s National Cyber Security Centre (NCSC) in its latest semi-annual report: the “dream job playbook”.
The timing also highlights the importance of ongoing cybersecurity awareness across the industry. Just two days before the Binance incident, the Crypto Valley Association (CVA) had hosted a cybersecurity event, bringing professionals together to address challenges and threats affecting the ecosystem.
How the “Dream Job” Playbook Works
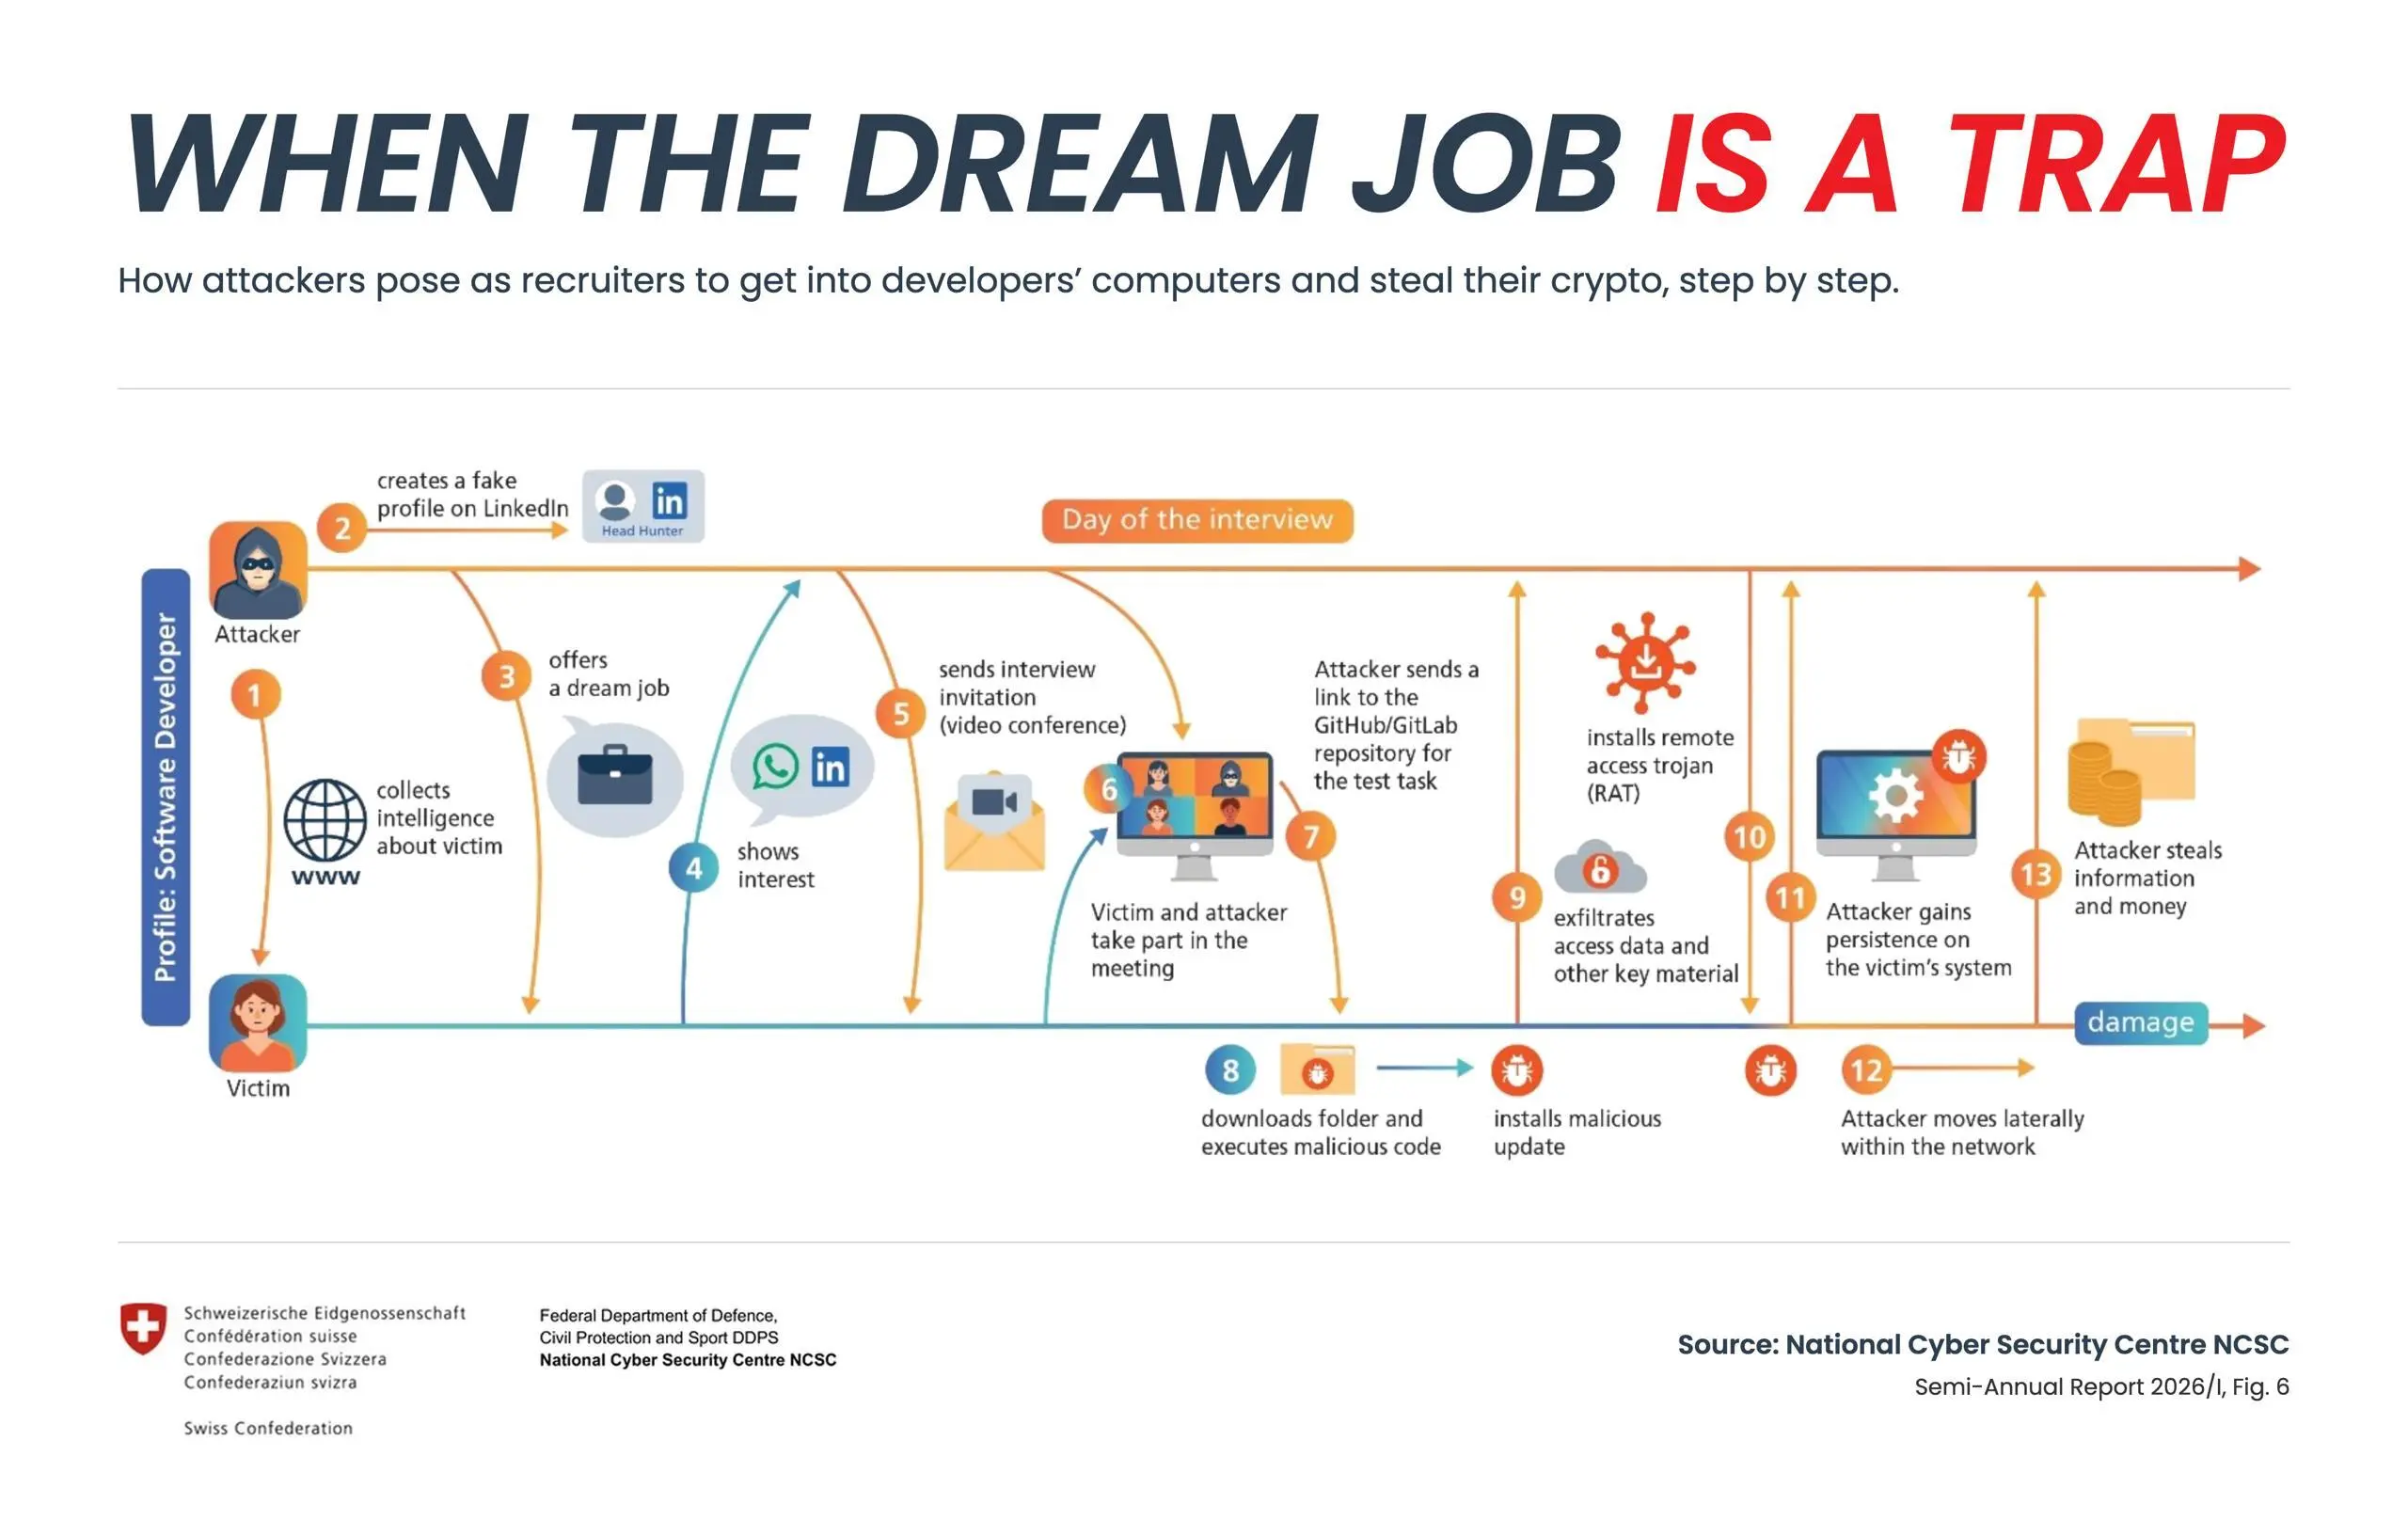
The attack often begins with a recruiter or headhunter approaching a professional on LinkedIn or another job platform with an attractive offer.
After one or more interview rounds, the candidate receives a technical assignment through a code repository. In other cases, a video interview connection suddenly drops, and the candidate is asked to install an update or a quick fix to continue.
In both scenarios, the downloaded file contains malware.
Once installed, it can steal credentials, authentication tokens and wallet keys, potentially giving attackers access to company systems and sensitive infrastructure.
What the NCSC Is Seeing in Switzerland
The NCSC's latest semi-annual report highlights the scale of this threat within the Swiss business environment.
Key findings include:
-
More than 20 reported cases over the past five years, mainly affecting the crypto sector, with targets ranging from engineers to managers.
-
Financial losses ranging from a few thousand francs to approximately CHF 60 million.
-
Underreporting remains a major concern: for every person who recognises the scam in time, another only realises what happened afterwards.
-
Multiple employees targeted: in some companies, several colleagues received similar approaches without informing their employers.
This last point is particularly concerning. Attackers rely on employees staying silent. People may feel uncomfortable admitting they considered another job opportunity, giving attackers more time to move through an organisation without being detected.
Three Steps to Reduce the Risk
While these attacks are becoming increasingly sophisticated, a few basic precautions can make a significant difference:
-
Keep work devices protected. Never run code, technical assignments or software updates received through an unsolicited recruitment process on devices connected to company systems or digital assets.
-
Verify job offers independently. If an opportunity seems unusually attractive, check the recruiter's identity and the company's legitimacy through separate, trusted channels.
-
Report suspicious activity. Inform your company's security team and report any suspicious contact to the NCSC, even if no damage has occurred. Early reporting can help prevent further attacks.
Why Cybersecurity Awareness Matters
The Binance incident is a reminder that cybersecurity is not only a technical issue. It also involves people, processes and everyday decisions.
For companies operating in the blockchain and digital asset sectors, staying informed about emerging threats is essential.
Through its Cybersecurity Working Group, the Crypto Valley Association provides a platform for industry professionals to exchange knowledge, discuss current challenges and explore practical approaches to strengthening cybersecurity across the ecosystem.
CVA regularly hosts events and discussions on relevant cybersecurity topics, creating opportunities for professionals and companies to learn from experts and stay informed about the threats facing the industry.
The recent timing of the CVA cybersecurity event is a timely reminder of why these conversations matter.
Stay prepared. Take part in CVA Cybersecurity Working Group events.
Stay informed:
-
Subscribe to our newsletter for the latest Crypto Valley updates.
-
Follow our Luma page to discover and join upcoming CVA events.
Sources: Binance Incident Report (November 2026); NCSC Semi-Annual Report 2026/I.